Skip to content

Product & App Development

Application Modernization & AI Code Rescue

A product can still have users after its development process stops working. The build breaks on current tools, updates introduce new problems, or AI-generated features behave differently from their demos. Our application modernization services start by inspecting the code, then restore a reproducible build and upgrade in stages around what current users need to keep doing.

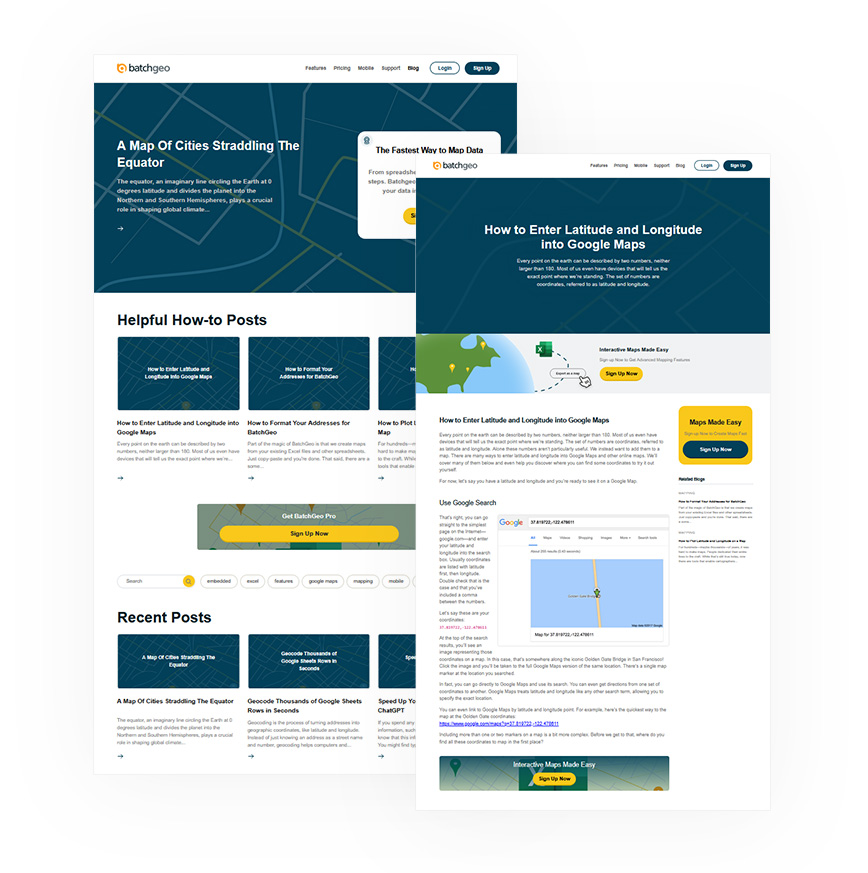
Batch Geo WordPress Design
BatchGeo · technical partner since 2021
Clients

Companies we’ve worked with.

Signs It Needs Attention

Signs your application needs modernization.

An AI-built application can show similar symptoms: features that appear complete but lead nowhere, fixes that break again and tests nobody has confidence in.

  • The app won’t build on current tools

    A dependency or development environment changed, and the team can no longer produce a repeatable build.

  • Updates cause unexpected failures

    There are few tests around important behavior, so a framework or package update risks breaking unrelated features.

  • Critical libraries have fallen behind

    Framework versions, SDKs and external services are no longer aligned with the product’s current platforms.

  • Knowledge left with the developers

    Undocumented code, inaccessible accounts and missing configuration now slow down every change.

  • Integrations are fragile

    Sign-in, payments, analytics, device connections or backend APIs fail in ways nobody can easily reproduce.

  • Releases are difficult to repeat

    The code may work on one machine, with signing, environment and deployment steps unclear to the current team.

Repair, Move or Rebuild

Application modernization services begin with an assessment.

We inspect the codebase, build and deployment process, tests, data flows, integrations and security risks before choosing a path. Legacy application modernization may mean repairing the existing structure, upgrading a component or replacing a larger section that can no longer support the roadmap. Legacy app modernization also requires a plan for existing data and users. We provide a written recommendation with the important unknowns and a sequence designed around the product’s current users.

  • Repair the working foundation

    Update dependencies, restore the build and test behavior the application must preserve.

  • Move a limiting component

    Replace a backend SDK, rebuild native project files or isolate an older renderer when that addresses the bottleneck.

  • Rebuild when the architecture requires it

    Define the behaviors, integrations and data that need to carry forward before planning a replacement.

Mobile App Rebuild

How we got a stalled mobile app building again.

The original developers of this mobile app were no longer available, and the code would not build on a current machine. Some dependencies and configuration were out of date or difficult to obtain. We created a current Expo-based native project, brought the existing source into it and revised the backend and device integrations. A replay harness now runs recorded sessions through the real integration and analytics paths, so the team can test important behavior without a physical device for every run. The app builds and runs on a current iOS simulator.

  • 326 passing tests

    Automated coverage grew from 26 test files to 56 suites.

  • 0 TypeScript errors

    Down from about 186.

  • 67 dependencies

    Updated, replaced or removed.

  • About 25 existing bugs

    Found and fixed, including failures in a core integration.

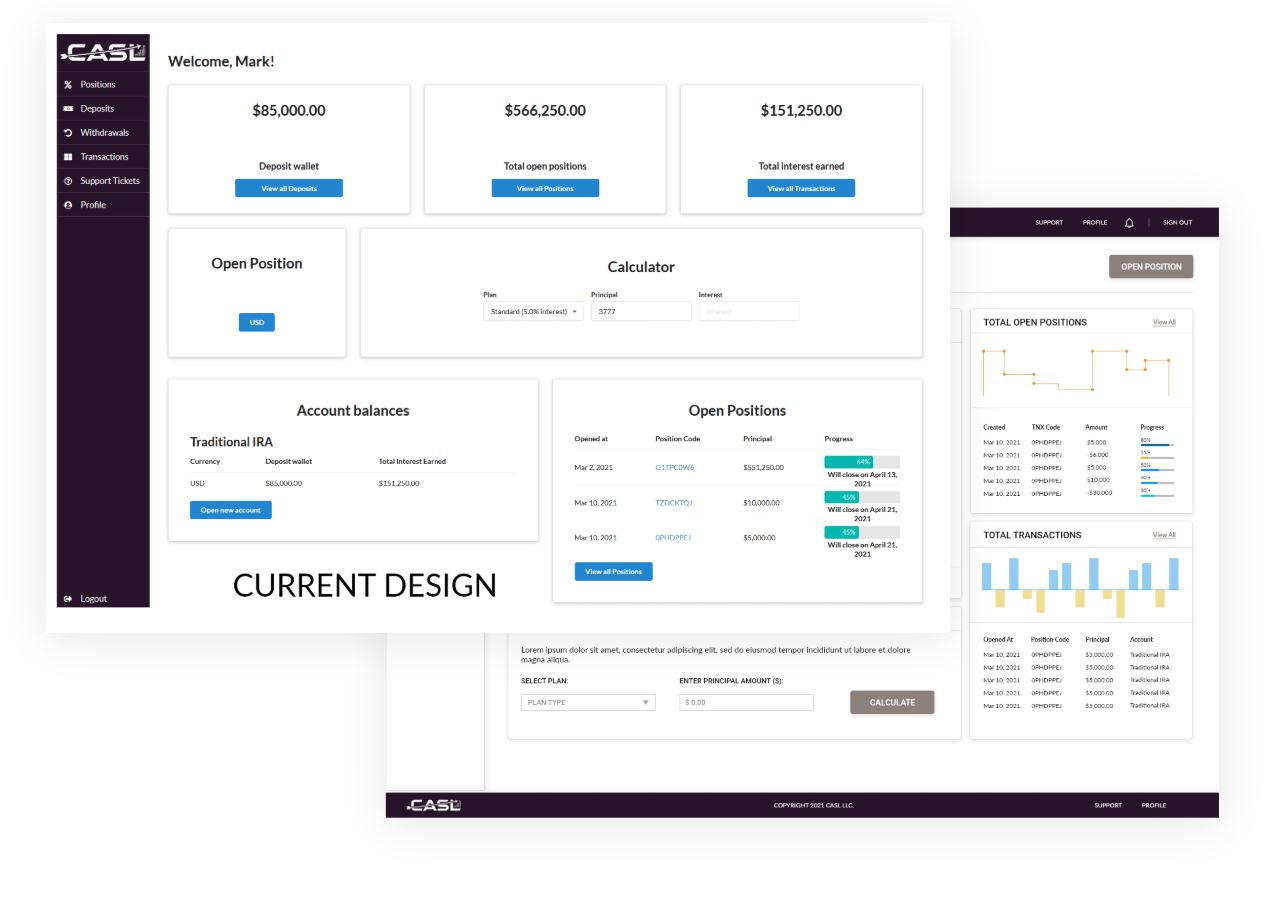
CASL member dashboard with balances, positions and transactions
Financial technology · Platform takeover

CASL: taking over a live investment platform and stabilizing it first.

CASL’s Ruby on Rails platform was already handling member accounts when we joined in March 2021, and its original developers were moving on. We audited the code and AWS infrastructure before adding features, then became the engineering and product support team for seven branded versions of the platform.

  • Stabilize. Fixed the scheduled jobs that were not closing investment positions reliably, cleaned duplicate records and repaired the automated tests.
  • Release process. Code review, automated tests and a staging deployment before production, with deployments moved to AWS container services.
  • Keep it running. When the pricing provider discontinued its API in 2023, we switched the data source so account valuations kept refreshing.
CASL, 2021 to 2023
18 months

Active development

2,360

Hours of development and product support

7

Branded instances from one codebase

Read the CASL case study
AI Code Rescue

AI code rescue for apps built with AI coding tools.

A research paper first published in June 2026 and revised in September collected 9,041 open-source applications built with AI coding agents. The researchers audited 200 publicly deployed applications and found 1,186 vulnerabilities; 91% of the audited applications contained at least one.

Our AI code rescue and vibe coding cleanup work has four parts: a CodeRaven-assisted audit with senior human review; security hardening around authentication, secrets and input validation; tests that independently verify behavior; and a development workflow the team can maintain.

  • A finished interface with missing behavior

    In one of our structured verification projects against an approximately 1,000-item specification, only 30–40% had been implemented. A payment flow ended at a blank screen; other data connections returned mock values.

  • Security rules left unstated

    The revised 2026 study identified recurring problems in access control, authentication and injection handling. We check that an application enforces those rules in its actual code and data flows.

  • A workaround that removes protection

    A change made to get a feature working can weaken authorization or error handling. In the revised study, 65.77% of the 1,186 identified vulnerabilities were rated critical or high severity.

  • Dependencies that do not exist

    Generated references can point to nonexistent or outdated packages. We check dependencies against actual registries, installed versions and the current build.

  • Errors hidden instead of handled

    A feature may appear functional while failures are ignored or concealed. We test what happens when a request, integration or authorization check fails.

What We Modernize

Web, mobile and backend code we modernize.

Our software modernization services focus on existing products. For a new build, see custom web applications; for taking over a live mobile product, see Mobile App Development; for existing engine projects, see Unity and game development.

  • Mobile

    React Native, Expo and Swift, including native project upgrades and platform integration work.

  • Web applications

    JavaScript, React, Node.js and Ruby on Rails, including application and API modernization.

  • PHP systems

    WordPress and custom plugins, CakePHP and the supporting services behind them.

  • Interactive software

    C#, older Unity projects and applications that need updated development tools or target platforms.

  • Backend and integrations

    Authentication, third-party APIs, data pipelines, payment systems and connected services.

  • AI-generated code

    Codebases that need verification, security work, testing and release practices.

How an Engagement Runs

Keep the product running while the code changes.

For a live product, we identify data and behavior to preserve and decide how updates will be staged, tested and rolled back if a release fails. The actual release sequence follows the architecture and the way people currently use the application.

  1. 01

    Assess

    We review source code, dependencies, platform versions, deployment, tests, integrations and data flow. When the build is broken, reproducing the failure may be the first milestone.

  2. 02

    Stabilize

    We restore a reproducible build, resolve blockers and add tests around behavior that must survive the work.

  3. 03

    Modernize

    We upgrade or replace the highest-impact components first and verify that the required workflows still operate as tools change.

  4. 04

    Hand over or continue

    We document the system and important decisions, hand over code when requested and support ongoing development if needed.

Getting Started

Find out what the current code can support.

Modernization assessment or AI code audit

We agree on the scope and deliverables first, then provide a price before the work begins. The output includes findings, critical unknowns and a written recommendation on what to repair, upgrade or replace.

  • Stabilization

    Restore a reproducible build, resolve blockers and add tests around the behavior users depend on.

  • Modernization in stages

    Upgrade or replace the highest-impact components first and check the required workflows at each stage.

  • Ongoing support and development

    We continue development and support, or hand over the code when you request it.

FAQs

Questions about application modernization.

What do application modernization services cost?

The cost depends on the age and condition of the code, available documentation, integrations, testing and platform requirements. The initial assessment or AI code audit has defined deliverables and a price agreed before work starts. Implementation is estimated from the findings.

How long does legacy application modernization take?

It depends on whether the build is reproducible, the number of outdated dependencies and what must keep working for users. We assess those constraints first and plan work in stages.

Should we rebuild the application or improve it?

We inspect the product before deciding. Repair and upgrade make sense when the underlying structure supports the roadmap. Replacing one component may resolve a specific blocker. A larger rebuild becomes appropriate when the architecture prevents necessary work.

Is an application built with AI coding tools salvageable?

Often, yes. We check the actual behavior, access controls, dependencies and tests, then stabilize the code that can be retained. A rescue may involve filling in missing connections, strengthening security and adding independent verification.

What does an AI code audit include?

It combines automated review through CodeRaven, our code review product, with senior engineering review. CodeRaven has reviewed every pull request our team has shipped since February 27, 2026. Findings are prioritized by risk and followed by recommendations for authentication, authorization, secrets, validation, testing and workflow improvements.

Will we have to rewrite everything?

A full rewrite is one possible outcome, and it is chosen only after an assessment of the existing code and product needs. Many modernization projects proceed through targeted fixes and staged upgrades.

Can you work with our developers?

We can review an existing codebase and define discrete remediation work. The audit and implementation scope establish responsibilities and handoff points.

Do you need the original developers?

No. Access to the repository, configuration, services and deployment accounts is more important. We reconstruct the build and document the missing steps as part of the assessment.

Will users be affected during modernization?

We identify essential behaviors and data, build test coverage around the vulnerable areas and plan staged releases with a recovery path. The goal is to reduce disruption while moving the technology forward.

Will you work on an app made with AI?

Yes. Our engineers build with AI coding tools themselves, and CodeRaven reviews the pull requests our team ships. We assess the implementation on what the code actually does, the risks it contains and what the product needs next.

Work With Us

Talk to our developers about your application.

Tell us what the product does, where updates are getting stuck and what the next release needs to support. We can assess the code and recommend a path forward.

Start a Conversation 4520 SE Belmont St, Suite 300
Portland, Oregon